The certification cycle, run properly, in one system.
CertifyPilot manages a certification body's work from application to recertification: contract review and audit time under IAF MD5, audit plans and checklists, findings, independent technical review and decision, and certificates your clients' customers can verify online.
No card required. Designed with an INAB-accredited certification body in Ireland.
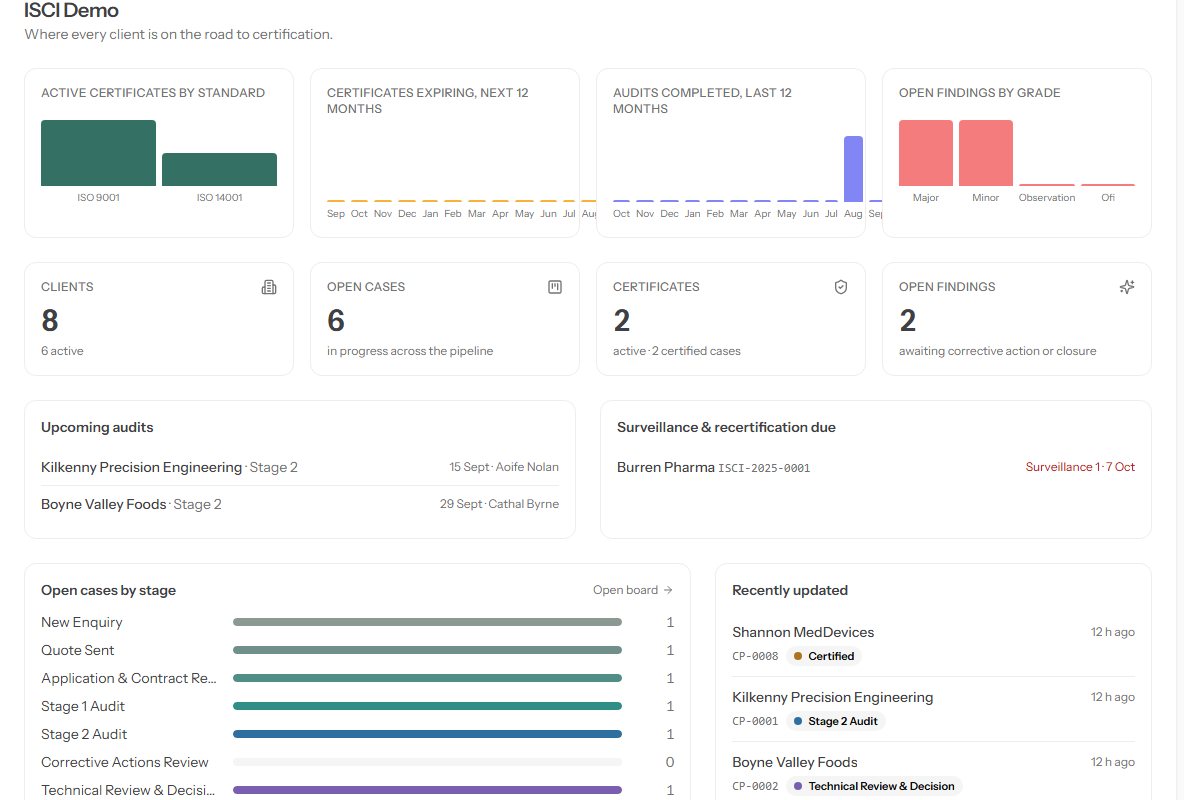
app.certifypilot.app/dashboard
ISO/IEC 17021-1 lifecycle
IAF MD5 · MD1 · ISO/IEC 27006 audit time
ISO 9001 · 14001 · 45001 · 27001 · 50001 · 22000
EU-hosted, GDPR processing terms
Application to quotation
Contract review that produces the audit days and the quote.
Personnel, sites, complexity, integrated standards and the influencing factors from IAF MD5 go in; Stage 1, Stage 2, surveillance and recertification days come out, with the fee from your own rate table. Each review is versioned and approved by a second person, and the quotation letter is generated from the approved version.
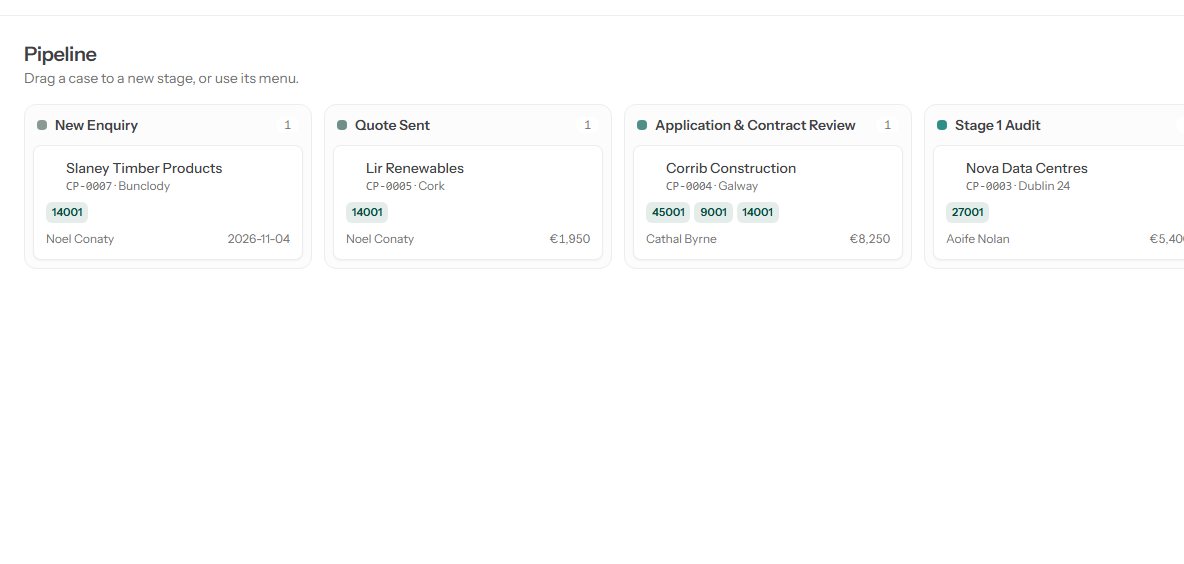
Cases move through the stages an accredited body uses, with every move logged
ISO/IEC 27006 and ISO 50003 variants for information security and energy
Transfer checklist for clients coming from another body
Pipeline
On the audit
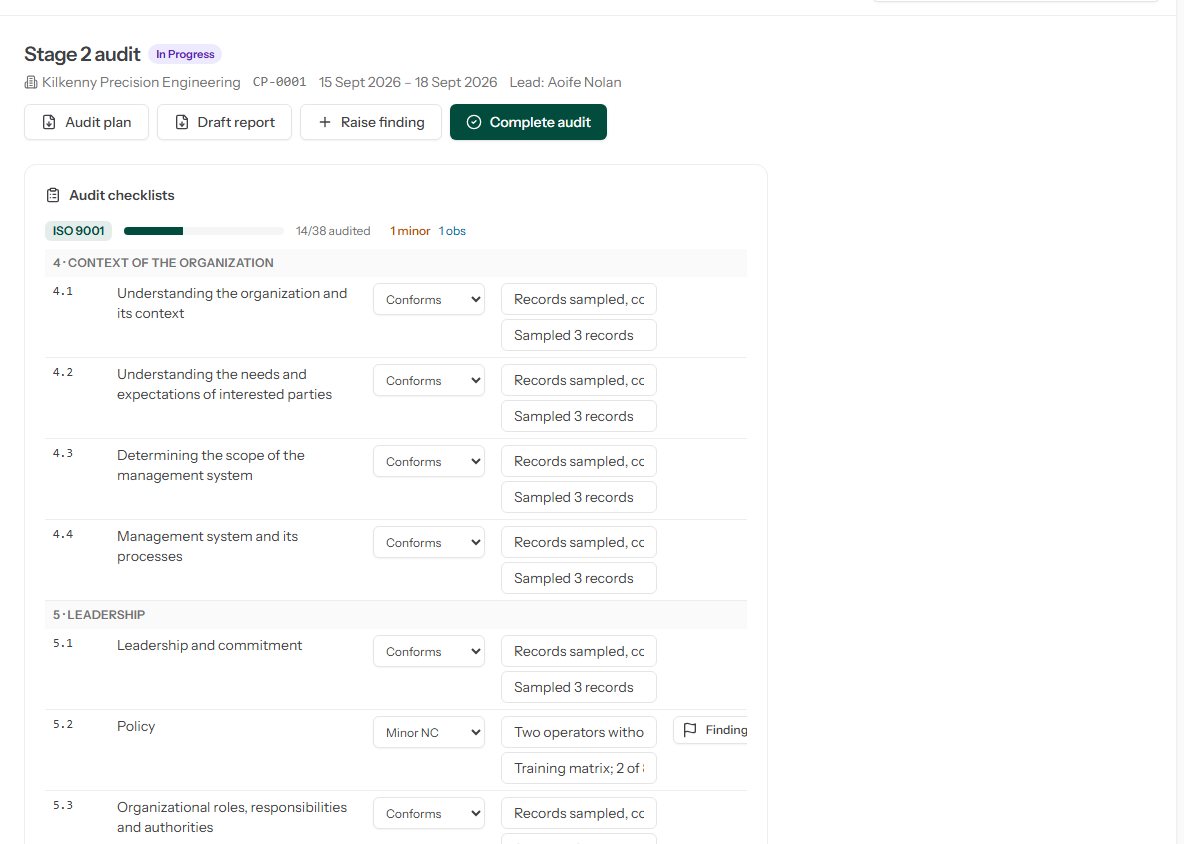
Clause-by-clause checklists, findings raised in place.
Auditors record a result, notes and the evidence sampled against each clause. A nonconformity becomes a finding with one click, the client responds through their portal with root cause and corrective action, and the lead auditor accepts or rejects. The audit plan and audit report are produced from the same record.
Assignments checked against each auditor's approved competence per standard
Impartiality declarations required before anyone audits, reviews or decides
Findings register across all clients: open, overdue, awaiting review
Stage 2 audit · checklist
Decision and certificate
Independent decisions and certificates that can be verified.
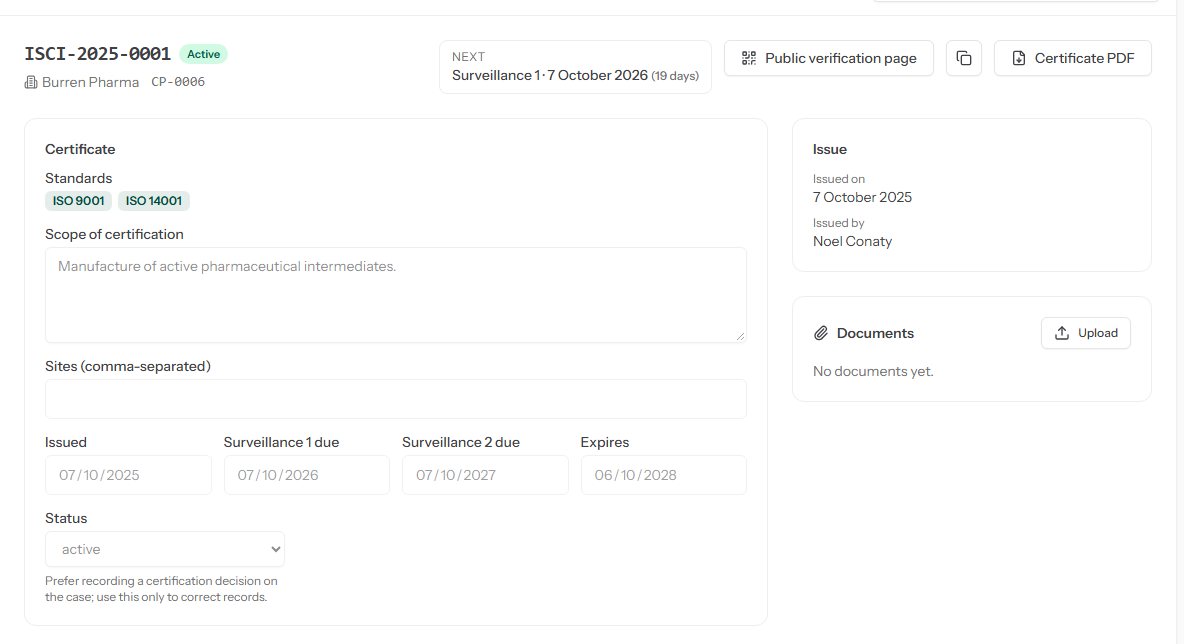
A technical reviewer who was not on the audit team completes a six-point review. The decision cannot be recorded by a team member, with an open major nonconformity, or against the reviewer's recommendation. The certificate is numbered, branded and carries a QR code to a public page showing its live status, scope and validity.
Three-year cycle with surveillance and recertification dates and reminders
Suspension and withdrawal reflected on the public record immediately
Register export for accreditation body and IAF CertSearch submissions
Certificate ISCI-2025-0001
Also included
The rest of what a body needs, without add-ons.
Competence matrixAuditor, lead auditor, reviewer and decision-maker competence per standard, with expiry.
Client portalClients see their audits and certificates and answer findings with evidence, no account needed.
Audit plan, report and quotation PDFsGenerated from the record, branded, filed and locked.
Documents and evidencePer client, case, audit, finding and certificate. Generated documents are immutable.
RemindersSurveillance due, expiry, audits next week, overdue findings. In-app and by email.
Your brandingLogo, colours, scheme marks and signatory on certificates, quotes and the sign-in page at your own address.
Search, timeline, exportsFind any client, case or certificate; see a case's full history; export every register to CSV.
Consultancy workspaceFor ISO consultants, or a group running a body and a consultancy with enforced separation.
Two-factor authenticationAuthenticator-app sign-in with recovery codes, required for administrators and reviewers.
Accreditation
Controls your assessor asks about, enforced by the system.
These are not policies you write and hope people follow. They are conditions the software checks before it lets a record be saved.
ISO/IEC 17021-1
Requirement
How CertifyPilot enforces it
§5.2
Impartiality
Conflict-of-interest declaration per case before any audit activity; a related consultancy's clients are flagged and cannot be certified for two years.
§7.1 – 7.2
Competence
No assignment as auditor, lead, reviewer or decision-maker without approved competence for that standard. Admin overrides are logged with a reason.
§9.1.3
Application review
Contract review with IAF MD5 audit-time determination, versioned, completed by one person and approved by another.
§9.2.3 · 9.4.8
Audit plan and report
Both generated from the audit record; the report is fixed and filed at completion.
§9.5
Certification decision
Decision-maker must not have taken part in the audit; requires a completed technical review that supports the decision and no open major nonconformity.
§9.6.1
Public information
Every certificate has a public verification page reached from its QR code, showing current status.
§8.4
Records
Immutable activity log on every record; generated documents cannot be edited; sign-ins logged with IP and device.
For ISO consultancies
The same platform, for the other side of the table.
Consultancies manage gap analyses, implementations, internal audits and retainers per client, with documents and dates, and hand a complete file to certification. Where a group operates both a body and a consultancy, the two workspaces are separated by design and the two-year rule is applied automatically.
IsolationEach body is a sealed workspace with its own hostname. Data is scoped at the database layer, not just in the interface.
Independent reviewAuthentication, tenancy and upload handling reviewed adversarially; findings fixed and covered by regression tests.
HostingEU data centre, TLS throughout, encrypted secrets, nightly backups, Cloudflare in front.
Questions
Common questions
Do we need to be accredited to use it?
No. The system is built to the level an accredited body needs, so a body preparing for accreditation starts with records and controls that already fit the assessment.
How is audit time calculated?
The IAF MD5 chart and multipliers for complexity, multi-site sampling and integrated management systems, plus the ISO/IEC 27006 and ISO 50003 variants. We validated the engine line by line against a working body's contract-review workbook.
Is the text of the ISO standards included?
Checklists carry clause numbers and headings. The requirement wording is ISO copyright and is not reproduced; bodies holding a licence can add it.
Can our existing register be imported?
Yes. Clients can be imported from a spreadsheet in Settings, and we load certificates and cases for Professional and Enterprise customers during onboarding.
What happens when the trial ends?
The workspace is paused and nothing is deleted. Choose a plan to continue where you left off.
See it with your own clients in it.
Start a trial and import your register, or book a walkthrough and we'll set it up with you.